Developer tool
lfpolicy
Review AWS Lake Formation permissions, explain access, and plan policy changes.
Review access before changing it
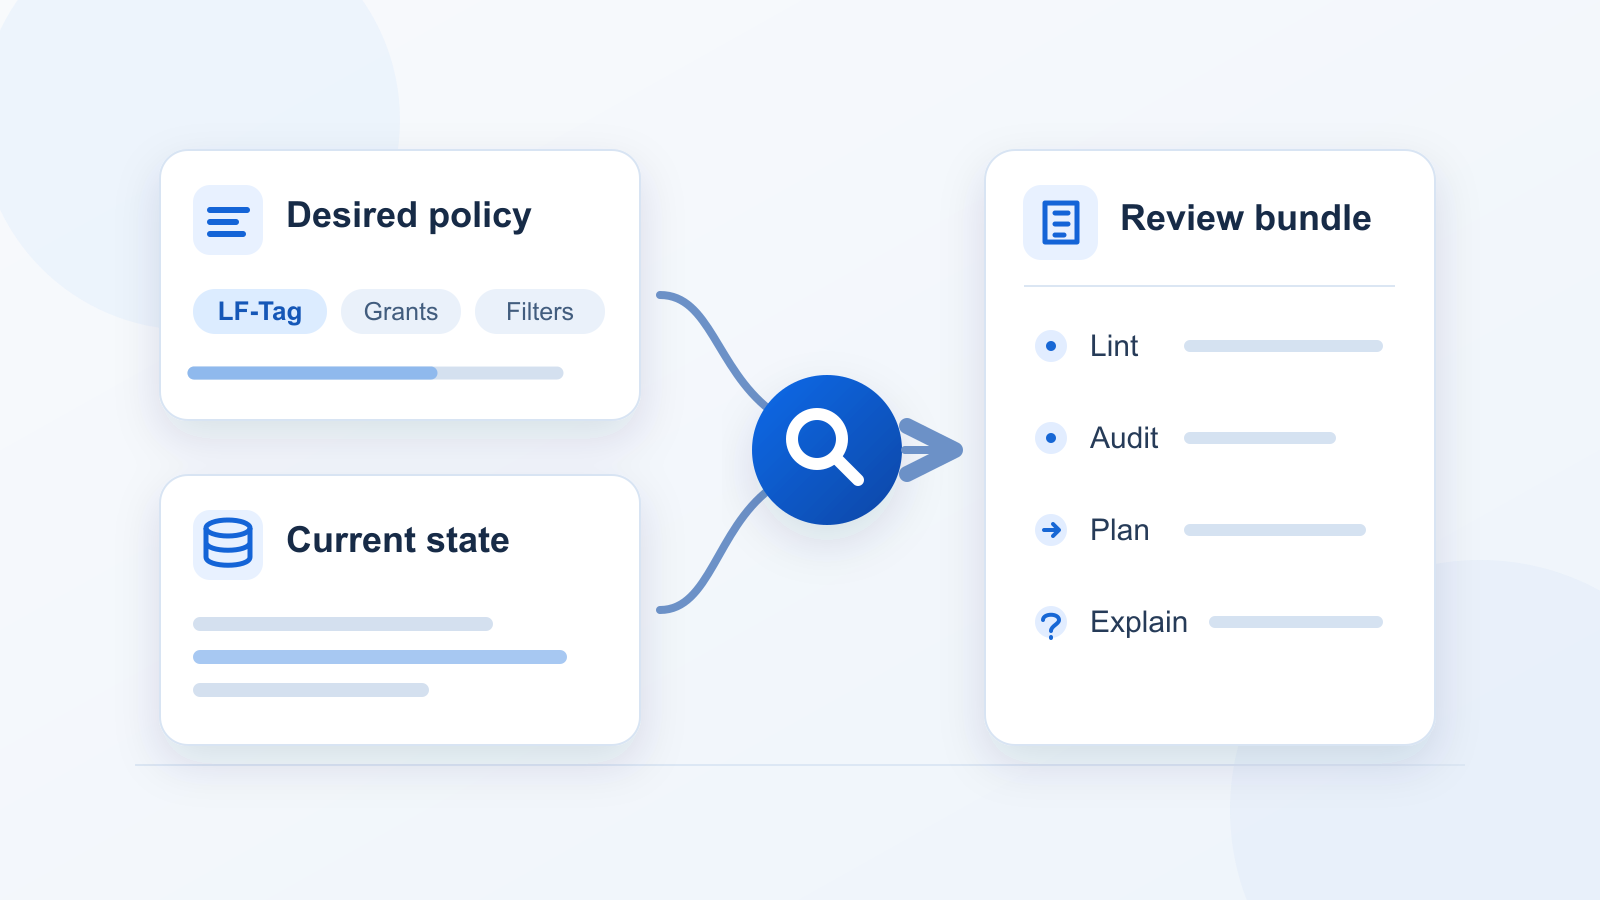
lfpolicy helps data platform teams compare a desired AWS Lake Formation policy with current permissions. It finds drift, explains why access exists or is missing, and prepares a reviewable change plan.
What a review covers
- Check LF-Tag definitions, resource assignments, grants, and data cells filters.
- Review policy files and snapshots offline, or inventory the relevant live AWS state with read-only access.
- Produce lint findings, an audit, a plan, access explanations, and a summary in one review bundle.
Start with an offline example
The GitHub quickstart generates sample desired and current state files, then shows how to build a review bundle without AWS credentials. Installation instructions are in the README; the package is available on PyPI.
Execution boundary
Live inventory reads AWS state. lfpolicy produces findings and plans; it does not apply grants or revokes. The operator or consuming service owns AWS changes. Plans omit potentially destructive revokes and tag removals unless the relevant option is enabled.